> ## Documentation Index
> Fetch the complete documentation index at: https://docs-staging-chore-actions-triggers-autoupdate.mintlify.site/llms.txt
> Use this file to discover all available pages before exploring further.
> Découvrez comment configurer les requêtes d’autorisation sécurisées par JWT (JAR) pour une application.
# Configurer les requêtes d’autorisation sécurisées par JWT (JAR)
export const AuthCodeBlock = ({filename, icon, language, highlight, children}) => {
const [displayText, setDisplayText] = useState(children);
const [copyText, setCopyText] = useState(children);
const wrapperRef = React.useRef(null);
useEffect(() => {
let unsubscribe = null;
function init() {
if (!window.autorun || !window.rootStore) {
return;
}
unsubscribe = window.autorun(() => {
let processedChildrenForDisplay = children;
let processedChildrenForCopy = children;
for (const [key, value] of window.rootStore.variableStore.values.entries()) {
const escapedKey = key.replaceAll(/[.*+?^${}()|[\]\\]/g, (String.raw)`\$&`);
let displayValue = value;
if (key === "{yourClientSecret}" && value !== "{yourClientSecret}") {
displayValue = value.substring(0, 3) + "*****MASQUÉ*****";
}
processedChildrenForDisplay = processedChildrenForDisplay.replaceAll(new RegExp(escapedKey, "g"), displayValue);
processedChildrenForCopy = processedChildrenForCopy.replaceAll(new RegExp(escapedKey, "g"), value);
}
setDisplayText(processedChildrenForDisplay);
setCopyText(processedChildrenForCopy);
});
}
if (window.rootStore) {
init();
} else {
window.addEventListener("adu:storeReady", init);
}
return () => {
window.removeEventListener("adu:storeReady", init);
unsubscribe?.();
};
}, [children]);
useEffect(() => {
if (!wrapperRef.current) return;
const originalWriteText = navigator.clipboard.writeText.bind(navigator.clipboard);
let isOverriding = false;
const handleClick = e => {
const button = e.target.closest('[data-testid="copy-code-button"]');
if (!button || !wrapperRef.current.contains(button)) return;
isOverriding = true;
navigator.clipboard.writeText = text => {
if (isOverriding) {
isOverriding = false;
navigator.clipboard.writeText = originalWriteText;
return originalWriteText(copyText);
}
return originalWriteText(text);
};
setTimeout(() => {
if (isOverriding) {
isOverriding = false;
navigator.clipboard.writeText = originalWriteText;
}
}, 100);
};
const wrapper = wrapperRef.current;
wrapper.addEventListener('click', handleClick, true);
return () => {
wrapper.removeEventListener('click', handleClick, true);
if (navigator.clipboard.writeText !== originalWriteText) {
navigator.clipboard.writeText = originalWriteText;
}
};
}, [copyText]);
return
{displayText}
;
};
export const codeExample1 = `POST https://{yourTenant}.auth0.com/api/v2/clients/{yourClientId}/credentials
Authorization: Bearer
Content-Type: application/json
{
"name": "Mes informations d’identification pour JAR",
"credential_type": "public_key",
"pem": "[YOUR PEM FILE CONTENT]",
"alg": "RS256"
}`;
export const codeExample2 = `PATCH https://{yourTenant}.auth0.com/api/v2/clients/{yourClientId}
Authorization: Bearer
Content-Type: application/json
{
"signed_request_object": {
"credentials": [{"id": "[YOUR CREDENTIAL ID]"}]
}
}`;
Pour utiliser les fonctionnalités de Highly Regulated Identity, vous devez avoir un Enterprise Plan avec le module complémentaire Highly Regulated Identity. Consultez la [tarification Auth0](https://auth0.com/pricing/) pour en savoir plus.
JWT-Les requêtes d’autorisation sécurisées par JWT (JAR) permettent de regrouper les paramètres de requête d’autorisation OAuth2 dans un seul paramètre de requête JWT, qui est ensuite signé pour en protéger l’intégrité.
Prérequis
Avant de configurer votre application pour utiliser JAR, vous devez [générer une paire de clés RSA](/docs/fr-ca/secure/application-credentials/generate-rsa-key-pair).
Vous devriez générer une paire de clés distincte pour chaque type d’utilisation des informations d’identification. Par exemple, n’utilisez pas la même paire de clés à la fois pour JAR et pour l’authentification Private Key JWT.
Vous pouvez configurer JAR pour une application avec l’Auth0 Dashboard et l’Management API.
Utilisez l’Auth0 Dashboard pour configurer votre application afin qu’elle utilise JAR avec des clés RSA générées au préalable.
1. Accédez à [Auth0 Dashboard > Applications](https://manage.auth0.com/#/applications).
2. Sélectionnez l’application que vous souhaitez utiliser avec JAR.
3. Sélectionnez l’onglet **Application Settings**.
4. Dans la section **Authorization Requests**, activez **Require JWT-Secured Authorization Requests**.
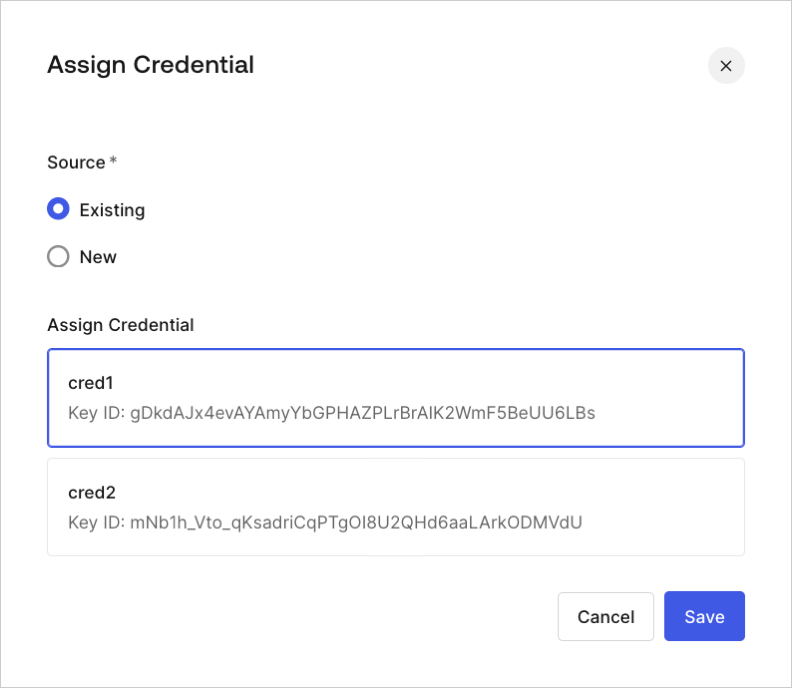
5. Si aucune information d’identification n’est attribuée et que des informations d’identification sont disponibles, vous serez invité à attribuer une information d’identification existante.
 6. Vous aurez aussi l’option d’attribuer une nouvelle information d’identification.
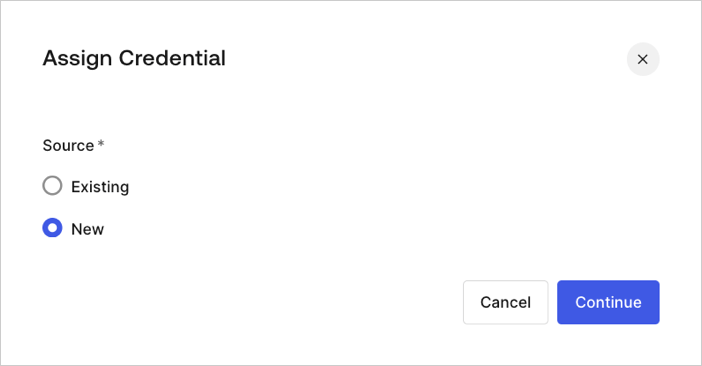 7. Ajoutez et attribuez une nouvelle information d’identification en téléversant une paire de clés RSA générée au préalable. Lorsque vous y êtes invité, entrez les renseignements suivants :
* **Name** : un nom pour identifier l’information d’identification
* **Public Key** : la clé publique du certificat X.509 au format PEM
* **Algorithm** : sélectionnez l’algorithme de signature JAR
* **Expiration Date** : définissez la date d’expiration de l’information d’identification
Utilisez la [Management API](https://auth0.com/docs/api/management/v2) pour configurer JAR pour votre application à l’aide de la propriété de configuration client `signed_request_object`. Cette propriété d’objet contient les champs suivants :
* `required` : force toutes les requête d’autorisation vers `/authorize` et `/oauth/par` à utiliser JAR. Pour en savoir plus, consultez [flux de code d’autorisation with JWT-Secured Authorization Requests](/docs/fr-ca/get-started/authentication-and-authorization-flow/authorization-code-flow/authorization-code-flow-with-jar).
* `credentials` : un tableau d’ID d’informations d’identification utilisées pour vérifier les signatures.
Le paramètre credentials se comporte de façon semblable au paramètre Private Key JWT `client_authentication_methods.private_key_jwt.credentials`, qui prend en charge la création d’informations d’identification lorsque vous créez une nouvelle application. Pour en savoir plus, consultez [Configure Private Key JWT](/docs/fr-ca/get-started/applications/configure-private-key-jwt).
Vous pouvez configurer JAR pour une nouvelle application ou une application existante au moyen de la Management API.
Lorsque vous créez une nouvelle application, configurez JAR en envoyant une requête POST avec `signed_request_object`. Dans cette requête POST, vous pouvez aussi enregistrer l’information d’identification client correspondante (c.-à-d. la clé PEM) :
```json lines theme={null}
POST https://{yourTenant}.auth0.com/api/v2/clients
Authorization: Bearer
Content-Type: application/json
{
"name": "My App using JAR",
"signed_request_object": {
"required": true,
"credentials": [{
"name": "My credential for JAR",
"credential_type": "public_key",
"pem": "[YOUR PEM FILE CONTENT]",
"alg": "RS256"
}]
},
"jwt_configuration": {
"alg": "RS256"
}
}
```
Lorsque vous mettez à jour une application existante, vous devez d’abord créer explicitement une information d’identification client. La requête POST suivante utilise le contenu de votre fichier PEM pour créer vos informations d’identification client pour JAR :
Assurez-vous que les sauts de ligne sont correctement encodés en JSON, sans mise en forme supplémentaire.
Ensuite, attribuez l’information d’identification client à la configuration client `signed_request_object`. La requête PATCH suivante associe vos informations d’identification client à `signed_request_object` :
En savoir plus
* [Flux du code d’autorisation avec requêtes d’autorisation sécurisées par JWT (JAR)](/docs/fr-ca/get-started/authentication-and-authorization-flow/authorization-code-flow/authorization-code-flow-with-jar)